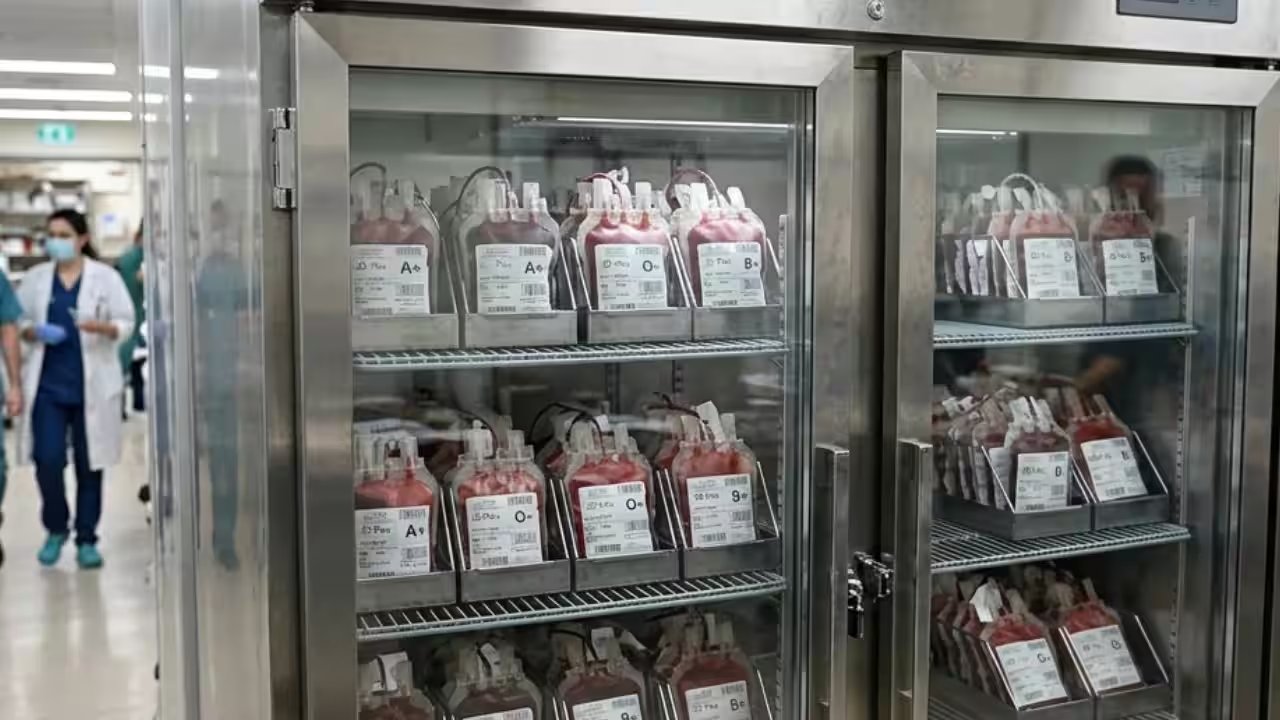
Hackers didn’t just break in; they tried to cook the evidence. On Monday, cyber-attackers remotely accessed the refrigeration controls at three French Blood Establishment (EFS) sites, cranking storage temperatures to dangerous levels. The goal was clear: spoil the plasma. But the EFS’s monitoring systems flagged the anomaly almost immediately. Staff intervened before a single bag of blood was compromised.
This isn’t an isolated glitch. It’s part of a coordinated, continent-wide assault on cold-chain infrastructure. Supermarkets in several European nations have already reported millions of euros in losses after similar hacks ruined freezers and fridges. The EFS confirmed the attack hit a supplier of their cooling equipment, though they haven’t yet identified the perpetrators. "No health consequences have been identified, and no blood products were lost," the EFS stated on Tuesday, emphasizing that all operations continued without interruption.
The stakes here are visceral. The affected facilities held plasma bags for transfusions and raw material for life-saving medicines. As a precaution, EFS moved all products from the targeted units to secure backup locations. While the immediate threat was neutralized, the vulnerability of critical medical infrastructure to remote cyber-tampering remains starkly exposed.
Now, the investigation shifts to the digital battlefield. France’s national cybersecurity agency, ANSSI, has launched a probe alongside the health ministry to trace the attack’s origin. With the EFS stepping up surveillance across its entire network, the next 48 hours will determine if this was a one-off test or the prelude to a larger campaign against Europe’s medical supply chain.